

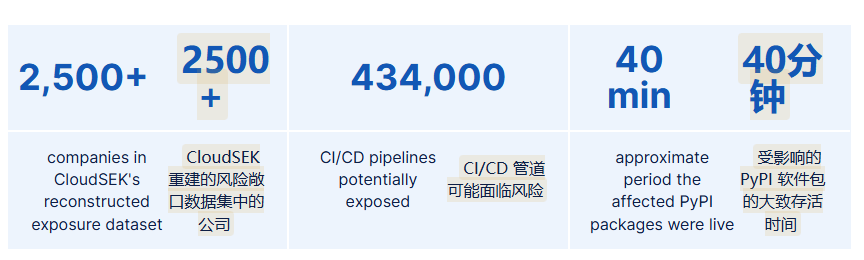
Technology media outlet Ars Technica published a post today (August 13), reporting that the LiteLLM API gateway poisoning incident that broke out in March this year affected approximately 2,500 companies worldwide during an attack window of about 40 minutes, resulting in the leakage of approximately 195TB of password data.
IT Home reported in March this year that LiteLLM, an AI infrastructure tool with an average of 95 million monthly installations, had been compromised through a supply chain poisoning attack.
LiteLLM is an open-source AI API gateway. As a key tool supporting the AI architectures of thousands of companies, it allows developers to call APIs from more than 100 providers, including OpenAI, Anthropic, and Azure, through a unified format.
According to data disclosed this week by security companies CloudSEK and Hudson Rock, attackers used the compromised version to collect and exfiltrate large quantities of password credentials during the approximately 40-minute attack window, affecting more than 2,500 organizations. They said this was the largest AI supply chain breach of 2026.
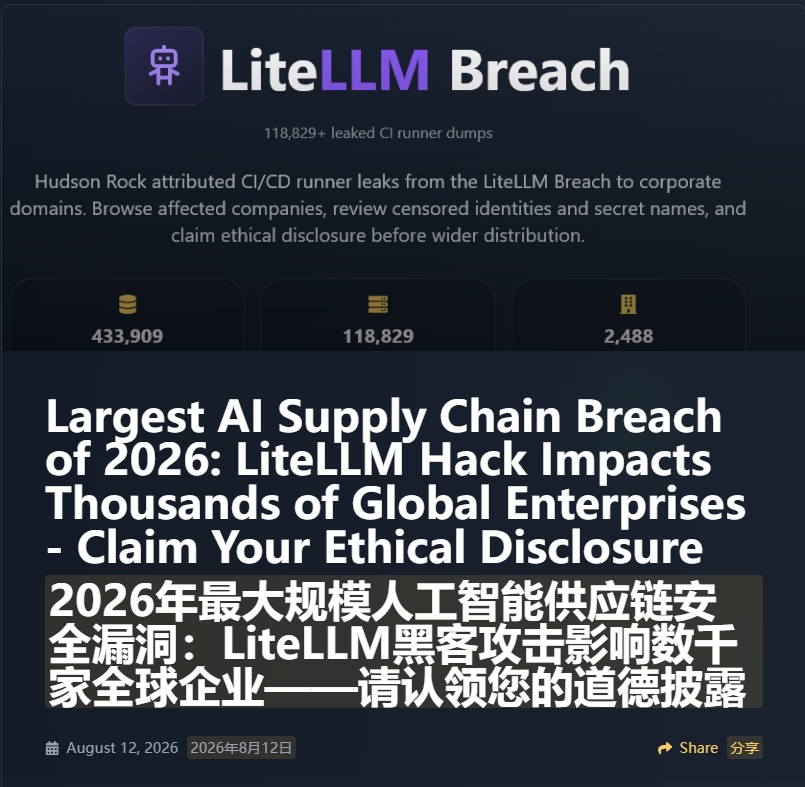
The exposed information included cloud keys, code repository tokens, SSH keys, Kubernetes keys, software package publishing credentials, environment variables, and AI provider keys.
The two companies analyzed a 195TB leaked file and found that approximately 434,000 credentials for CI/CD (continuous integration/continuous delivery) software pipelines were exposed in the security incident. These credentials were scattered throughout the massive dataset and involved a large number of organizations running LiteLLM.
Regarding the affected companies and institutions, the researchers said there was sufficient evidence that the following companies were impacted. The complete list can be viewed here:
Nvidia Corporation
Amazon Web Services (AWS)
Samsung Electronics
samsung.com
Salesforce
Cisco Systems, Inc.
F. Hoffmann-La Roche AG
ServiceNow
Siemens AG
S&P Global
Airbus US Space & Defense
John Deere
Regeneron Pharmaceuticals, Inc.
London Stock Exchange Group (LSEG)
Thomson Reuters
FedEx
Munich Re munichre.com
MediaTek Inc.
Volkswagen AG
Deloitte
The Kroger Co.
Siemens Energy
Thales Group
X (formerly Twitter)
Zscaler, Inc.
Epic Games
Orange S.A. Southern Australian Orange County
HP Inc.
Philips
Fortum Oyj
Vodafone Group Plc
Carl Zeiss AG
Deutsche Bahn AG
NGINX
BT Group
Liebherr
Krungthai Bank Public Company Limited
Roku
References
Largest AI Supply Chain Breach of 2026: LiteLLM Hack Impacts Thousands of Global Enterprises - Claim Your Ethical Disclosure
2,500+ Companies and 434,000 CI/CD Pipelines Exposed in the Largest AI Supply Chain Breach of 2026
Affected organisations