

According to foreign media outlet TechCrunch today (the 31st), thanks to internal AI tools, Google fixed more security vulnerabilities in Chrome in just one month than the total number fixed over the previous two years.
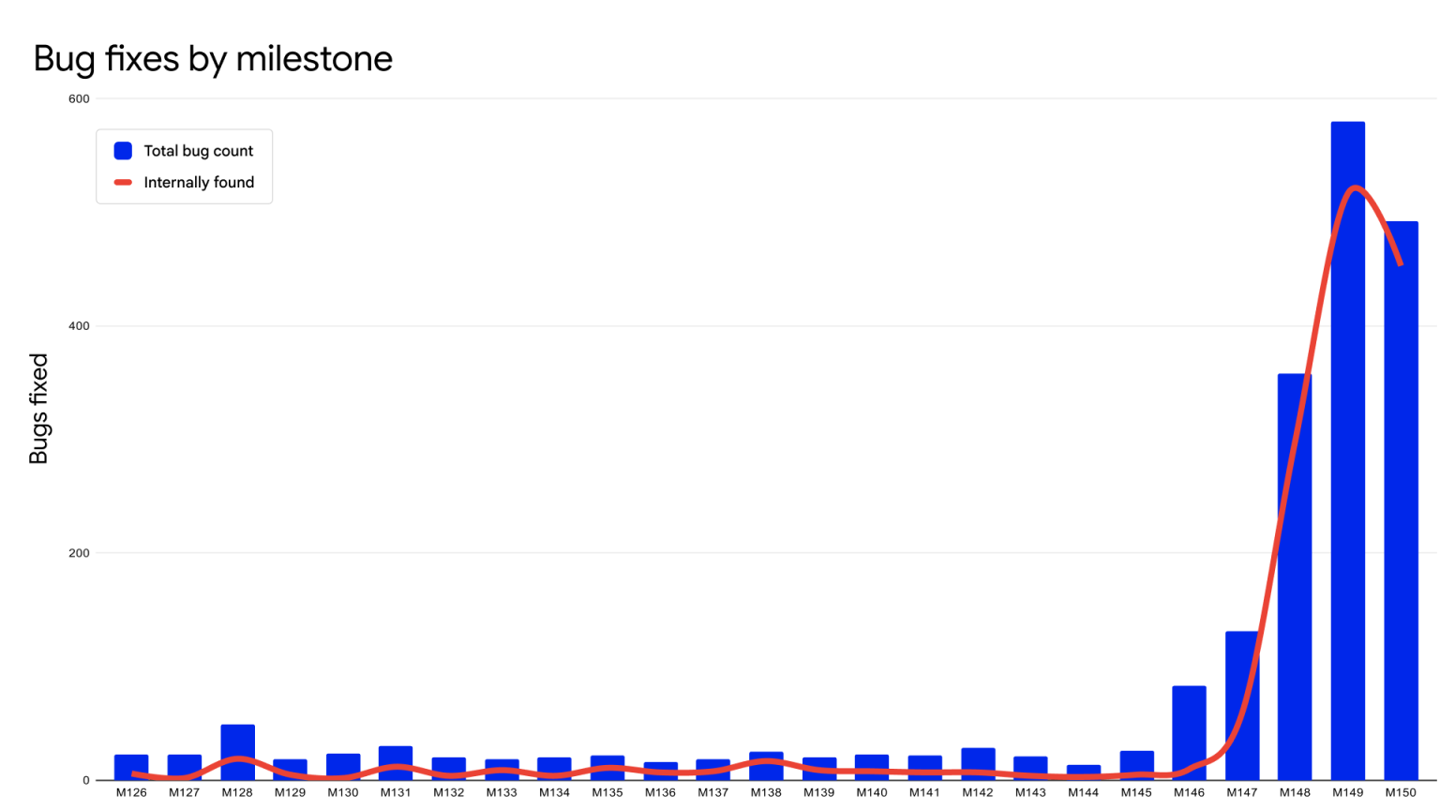
On the 30th local time, Google announced that Chrome 149 and Chrome 150, released in June, fixed a total of 1,072 security vulnerabilities. The 23 Chrome versions released over the previous two years fixed a combined 1,036 vulnerabilities, fewer than the total fixed by the two latest versions.
Since the emergence of large language models, cybersecurity experts have repeatedly warned that AI will discover massive numbers of vulnerabilities at an ever-increasing pace, with the number of vulnerabilities potentially growing exponentially. Facing malicious hackers who also use AI, security teams must likewise rely on AI to discover and fix problems in advance.
A chart in a Google white paper shows that the number of vulnerabilities discovered and fixed in Chrome is rising rapidly. The white paper explains how Google uses AI to find security flaws and shorten remediation times.
Chrome 126 was released in June 2024, while Chrome 149 and Chrome 150 were launched last month. Google refers to each official Chrome release as a “milestone.”
Doug Turner, Chrome’s engineering director, said that large language models have fundamentally changed the cost structure of cybersecurity, turning vulnerability discovery into an automated, industrial-scale operation. “By using models such as Gemini, we can fix vulnerabilities before they are exploited, stay ahead of our adversaries, and further improve Chrome’s security with every update.”
Google is not the only company to have experienced a similar change. Earlier this month, Microsoft announced that its product lines had fixed a record 570 security vulnerabilities in a single routine “Patch Tuesday” update. Microsoft believes that the internal use of AI was an important reason for the sudden surge in the number of fixes.
Apple has not yet shown the same exponential growth. Independent statistics show that Apple has fixed 482 product vulnerabilities so far in 2026. At the current pace, Apple’s annual total could reach or exceed last year’s figure, roughly returning to the level seen in 2015.