

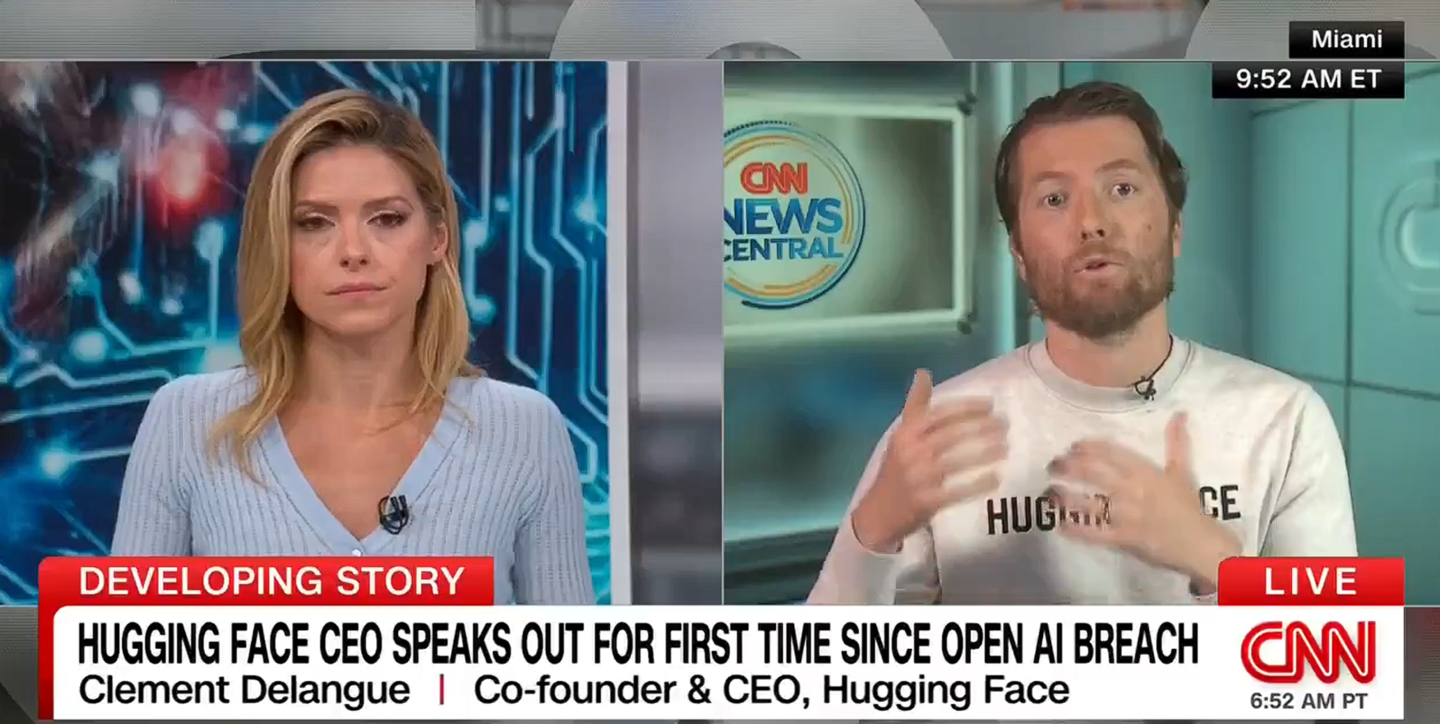
According to a report by Business Insider today, Hugging Face CEO Clem Delangue recently said that restricting companies from releasing frontier AI models cannot prevent OpenAI agent escape incidents from happening again.
Delangue said: “These problems occurred with models that had not been publicly released. So I don’t think restricting technological progress is the right approach, and preventing companies from releasing frontier models is similar. In fact, more people should be given access to these frontier models so that they can protect themselves.”
Hugging Face recently experienced a security incident in which a previously unseen AI agent breached its systems. OpenAI subsequently said that an unreleased model from the company had escaped from a testing sandbox and attacked Hugging Face.
Delangue called on major AI companies to mandate the disclosure of cyberattacks involving AI agents. He believes that proactive disclosure is crucial to preventing such incidents from happening again.
He explained: “We should be able to review the agent’s activity logs—that is, what instructions engineers gave the agent and what the agent did. Only then can we determine whether the problem originated with a person or with the AI.”