

What Reverify Does
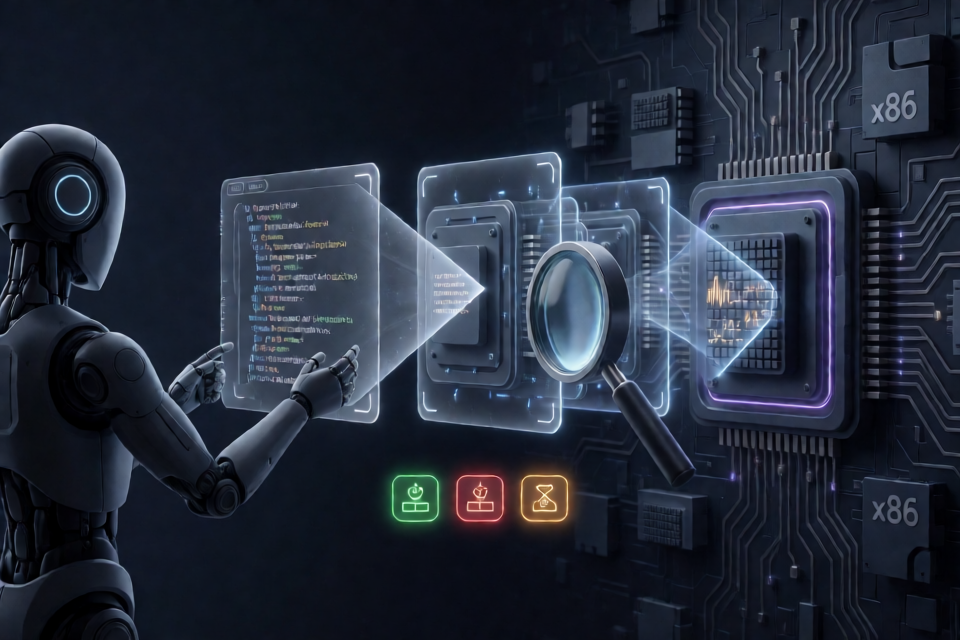
Reverify is an AI-assisted reverse-engineering toolkit designed to reduce hallucinations during binary analysis. Instead of trusting a language model's reconstruction, Reverify treats it as a hypothesis and checks it against the actual binary.
The workflow is simple: the model proposes, and deterministic tools verify. Reverify can disassemble bytes, scan patterns, parse executable formats, extract strings, emulate code, and inspect wire formats. A checked claim receives one of three results: VERIFIED, REFUTED, or INCONCLUSIVE, together with observed evidence.
Use Reverify only for authorized reverse engineering, such as malware analysis, CTF challenges, interoperability research, and software you own or have permission to inspect.
Key Features
- Deterministic verification: Claims are judged against bytes observed in the target binary rather than accepted from an AI-generated explanation.
- Executable parsing: Inspect PE, ELF, and Mach-O files, including architecture, entry point, sections, imports, and exports where supported.
- Disassembly and emulation: Analyze x86, x64, ARM, and ARM64 code, with capabilities depending on the active backends.
- Pattern and string analysis: Scan AOB patterns with
??wildcards and extract ASCII or UTF-16LE strings with offsets. - Protocol inspection: Decode Protobuf and TLV data without requiring a schema.
- Reverse-engineering utilities: Generate Frida hooks, create aligned hex dumps, and produce binary diffs or patches.
- Agent integration: Run Reverify as a Model Context Protocol server for tools such as Claude Code and Cursor.
- Pure-Python fallback: The base package works without Ghidra or mandatory native analysis engines.
Installation and Setup
Install the Pure-Python Core
Install the CLI and MCP server from PyPI:
pip install reverifyThis provides the pure-Python core and is the simplest way to begin.
Install the Optional Mature Engines
For enhanced parsing, disassembly, and emulation, install the full extra:
pip install "reverify[full]"The full installation enables Reverify to use Capstone for disassembly, Unicorn for CPU emulation, and LIEF for PE, ELF, and Mach-O parsing. If these packages are unavailable, Reverify falls back to its pure-Python implementation.
Check which engines are active:
reverify backendsRun Directly from a Checkout
The repository can also be used without installing the package:
python reverify/cli.py auto sample.bin --json
python reverify/cli.py parse-pe sample.exe --json
python reverify/cli.py disasm 90505831C0C3 --arch x86_64
Basic Binary Triage
Start with the auto command to detect the file format and architecture, inspect sections, and report notable strings:
reverify auto sample.bin --jsonThe --json option is useful when another script, CI job, or AI agent needs to consume the result programmatically.
For focused executable parsing, use parse for PE, ELF, or Mach-O files:
reverify parse sample.bin --jsonFor a Windows executable, the dedicated PE parser can inspect PE32 or PE32+ headers, imports, and exports:
reverify parse-pe sample.exe --jsonDisassembling Raw Bytes
The disasm command can decode hexadecimal machine code. This example analyzes a short x86-64 sequence:
reverify disasm 90505831C0C3 --arch x86_64Disassembly is useful for checking whether a proposed instruction sequence matches the bytes. Reverify can also disassemble code from a binary section, allowing claims to be tied to file contents rather than an isolated model-generated interpretation.
Using the Verification Loop
A Reverify claim is a structured hypothesis about a binary. The verify command evaluates the claim and returns its status with the evidence the toolkit observed.
Verify an Instruction Sequence
The following claim checks whether the bytes at offset 4096 decode to a function prologue beginning with push, mov, and sub:
reverify verify sample.bin --claim '{
  "kind": "instructions",
  "offset": 4096,
  "mnemonics": ["push", "mov", "sub"],
  "note": "function prologue"
}'
Reverify does not merely repeat the proposed interpretation. It reads and disassembles the relevant bytes, then reports whether the requested mnemonic sequence is supported.
Verify an Emulated Result
You can also test a behavioral claim by executing machine code in the emulator and checking its resulting registers:
reverify verify - --claim '{
  "kind": "emulate_result",
  "code": "b805000000b90300000001c8c3",
  "arch": "x86",
  "expect_registers": {"eax": 8}
}'
This verifies that the supplied routine leaves eax equal to 8. It is a stronger check than accepting a model's description of what the instructions appear to compute.
Available Claim Types
Reverify supports these claim kinds:
bytes_atchecks bytes at a specified location.pattern_presentchecks whether a byte pattern exists.string_presentchecks for a string in the binary.instructionschecks a proposed instruction sequence.emulate_resultchecks expected register results after emulation.protobuf_fieldchecks a Protobuf field claim.pe_importchecks a PE import claim.
Batch Verification and CI Gating
For larger investigations, place multiple claims in a JSON file and verify them together:
reverify verify sample.bin --claims-file claims.jsonThe CLI exits with a non-zero status if any claim is refuted. This behavior makes it suitable for CI pipelines and automated agent workflows: a reconstructed structure or routine can be rejected before it is published or used by a later step.
A practical workflow is:
- Use
auto,parse,strings, ordisasmto collect initial evidence. - Have an analyst or model formulate narrowly scoped claims.
- Store related claims in a JSON file.
- Run
verifyand inspect everyREFUTEDorINCONCLUSIVEresult. - Revise the reconstruction and repeat until the supported claims are grounded in observed evidence.
Additional Analysis Commands
Reverify includes several focused commands that can support the verification process:
- Pattern scanning: Use
pattern-scanfor AOB searches containing exact bytes and??wildcards. - String extraction: Use
stringsto locate ASCII and UTF-16LE strings and retain their offsets. - Micro-emulation: Use
emulateto inspect CPU register and stack behavior. - Wire-format dissection: Use
decode-protobufordecode-tlvfor schema-less data analysis. - Frida integration: Use
gen-hookto generate an interceptor script. - Raw inspection: Use
hexdumpfor an aligned view of binary data. - Change analysis: Use
diff-patchfor binary differences and patch generation. - Boundary auditing: Use
audit-boundaryfor defensive filesystem and SSRF boundary checks.
Closing the Loop with Reconstruction
The reconstruct command implements Reverify's closed-loop approach: a model proposes claims, the deterministic tools judge them, and the process iterates toward a grounded result. This is preferable to asking a model for a complete structure or algorithm and treating its first response as authoritative.
For reliable results, keep claims small and testable. A claim about exact bytes, a short instruction sequence, an imported function, or a register result is easier to verify and revise than a broad narrative about an entire binary.
Connecting Reverify to AI Agents
Start the MCP server from a repository checkout with:
python reverify/mcp_server.pyYou can then configure an MCP-compatible client such as Claude Code or Cursor to launch the server. The agent can call Reverify's parsing, disassembly, scanning, and verification tools directly.
The MCP tool re_verify_claim exposes the same verification loop to agents. This allows an agent to submit a hypothesis, receive VERIFIED, REFUTED, or INCONCLUSIVE, and revise its analysis before reporting a conclusion.
Advanced Tips
- Check active backends first: Run
reverify backendsbefore an analysis so you know whether Capstone, Unicorn, and LIEF are available. - Prefer JSON output: Use
--jsonwhen results will be parsed by scripts, agents, or CI systems. - Separate observation from interpretation: Record offsets, bytes, decoded instructions, and register states before writing a higher-level explanation.
- Treat inconclusive results honestly: An
INCONCLUSIVEresult is not verification. Gather more evidence or narrow the claim. - Batch related assertions: Put structural and behavioral checks into a claims file so that one refuted assumption can stop an automated reconstruction.
- Use emulation for behavioral claims: If a claim says what a routine computes, verify the expected register state rather than relying only on disassembly.
- Use the pure-Python fallback for portability: Begin with the base package, then install
reverify[full]when mature native engines are required.
Conclusion
Reverify makes AI-assisted reverse engineering more defensible by requiring important claims to survive deterministic checks against the binary. Its CLI supports quick triage, parsing, disassembly, pattern scanning, emulation, and batch verification, while its MCP server gives AI agents access to the same evidence-based workflow. The result is analysis grounded in observed bytes rather than confident guesswork.
Reverify is MIT licensed and available from PyPI.