
- Monthly visits
- 0
- Pricing
- Free & Paid
- Listed
- 2026-04-17
- Updated
- 2026-08-25
01Product Positioning
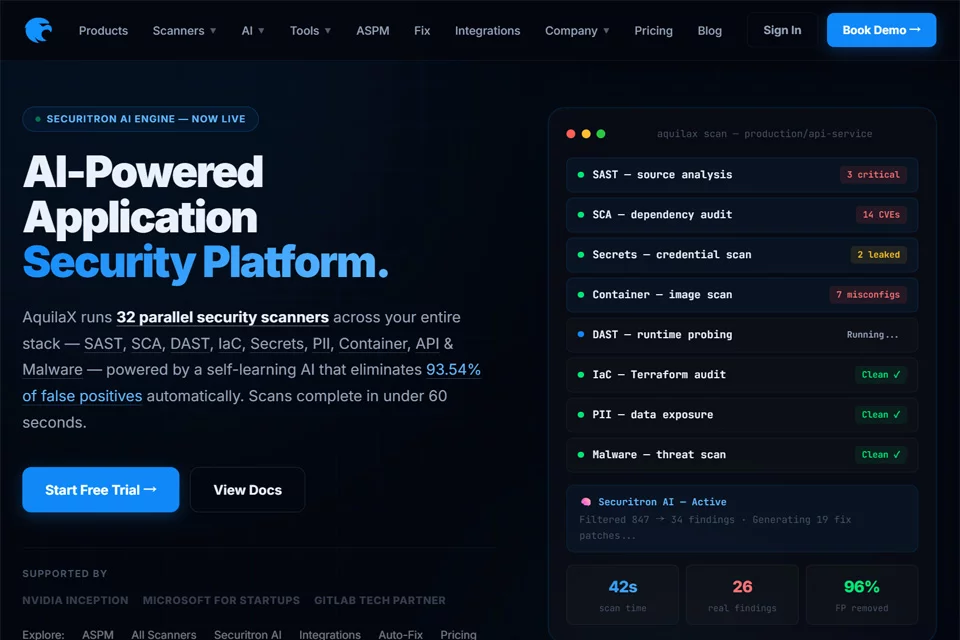
AquilaX is an AI-powered code security audit engine for development teams, security auditors, and startups. It brings code checking and container environment analysis into one workflow, helping teams identify potential security issues during development or before delivery.
The product offers free and paid plans. The applicable scope should be based on the current product page and plan details.
02Key Features
The product combines multiple scanning modules to check static code and container environments, identifying risks such as hardcoded secrets and personal information that could lead to data leakage.
For detected risks, AquilaX can generate remediation suggestions. Its models also analyze the team's business logic to help reduce alerts that do not match the project's actual circumstances.
03Use Cases
Development teams can use it for security checks before code submission, change merging, or release as an auxiliary step in the development workflow.
Security auditors can use scan results to organize issues requiring attention, while startups can use it for preliminary code and container environment checks when security resources are limited. Important systems should still be supported by manual audits and other testing methods.
04Usage Considerations
Scanning tools identify potential risks, and the results must be reviewed by people familiar with the project architecture and business rules. They should also confirm whether the remediation suggestions apply to the current code. Changes to container configurations, runtime environments, and dependencies may affect the results.
Before use, confirm the integration method according to the team's code hosting, deployment, and audit processes. Carefully review the feature scope, scanning limitations, and data handling details of the free and paid plans.
© Disclaimer: domains and linked content may change over time. AIEZZ does not control third-party websites. Review external content and risks independently.
User reviews0